Armor Eye SIEM
In-build enterprise SIEM that aggregates and analyses activity across the whole infrastructure to surface threats and vulnerabilities before an attacker uses them.
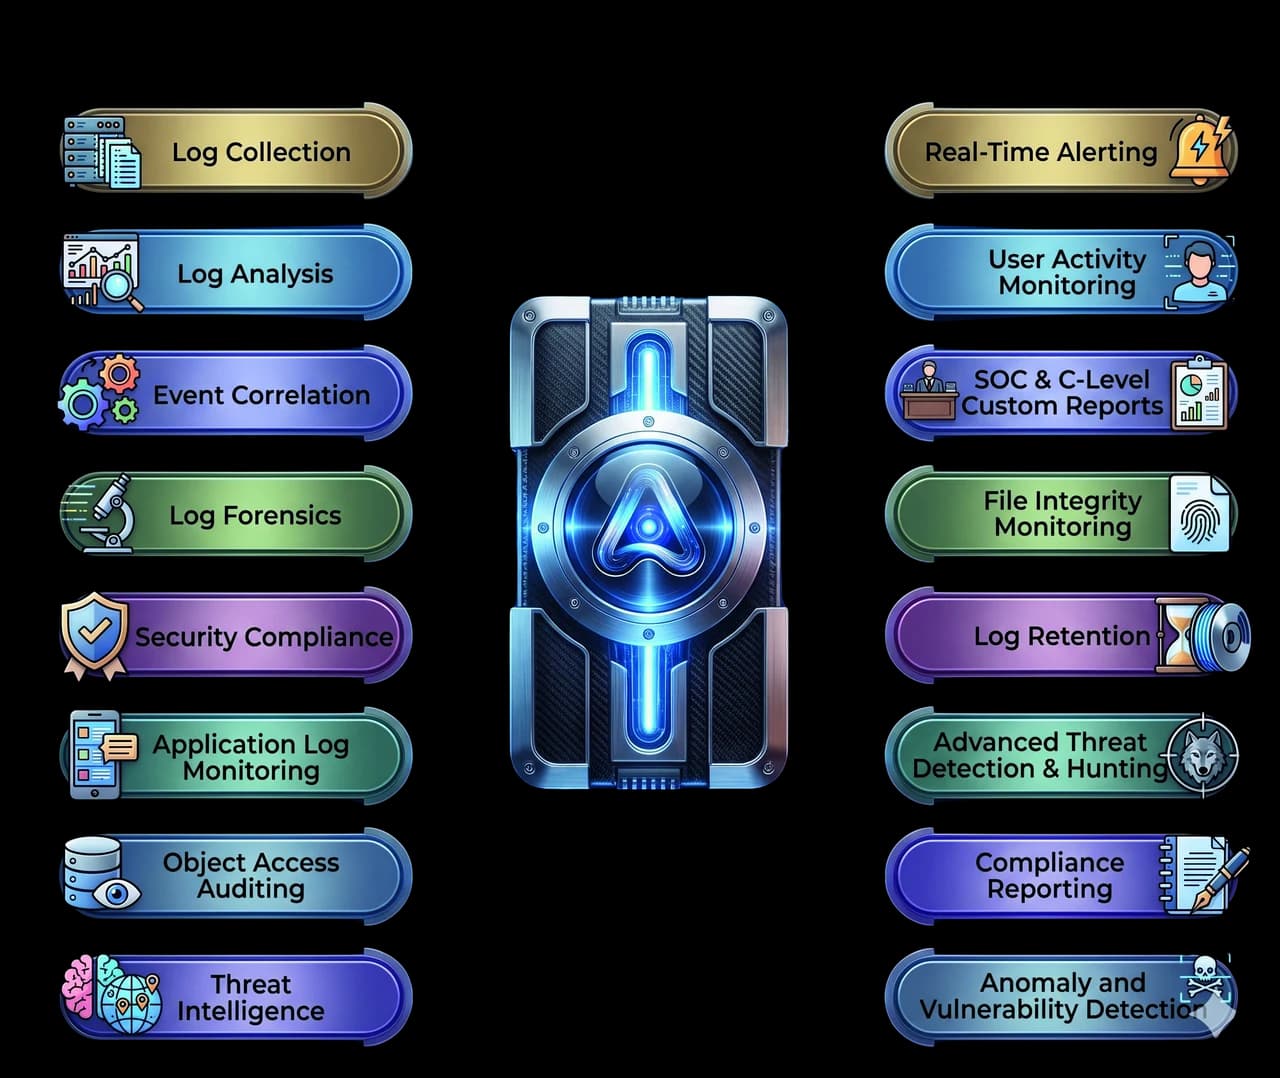
Armor Eye SIEM collects security data from network devices, servers, domain controllers and mobile devices, correlates it, and shows where the organisation is exposed. It is built for teams that need real detection plus the audit trail a compliance framework asks for.
- Threats and misconfigurations surfaced before exploitation
- Audit evidence ready for six compliance frameworks
- One console covering network, server, AD and mobile estate
- Web
- Desktop
What Armor Eye SIEM Does
Log Analysis & Log Management
Collection, correlation, forensics and retention across every source.
Security & Log Data Analytics
Turns raw event volume into prioritised, readable signal.
Intrusion & Vulnerability Detection
Advanced threat detection and hunting, plus anomaly detection.
Configuration Assessment (SCA)
Continuous checks against secure-configuration baselines.
Custom Dashboards & Reporting
SOC and C-level reporting views built per audience.
Compliance Reporting
ISO 27001, GDPR, HIPAA, NIST, PCI DSS and NESA reporting out of the box.
File Integrity & Activity Monitoring
User activity, application logs and object-access auditing.
Real-Time Alerting
Alerts the moment correlation rules or thresholds trip.